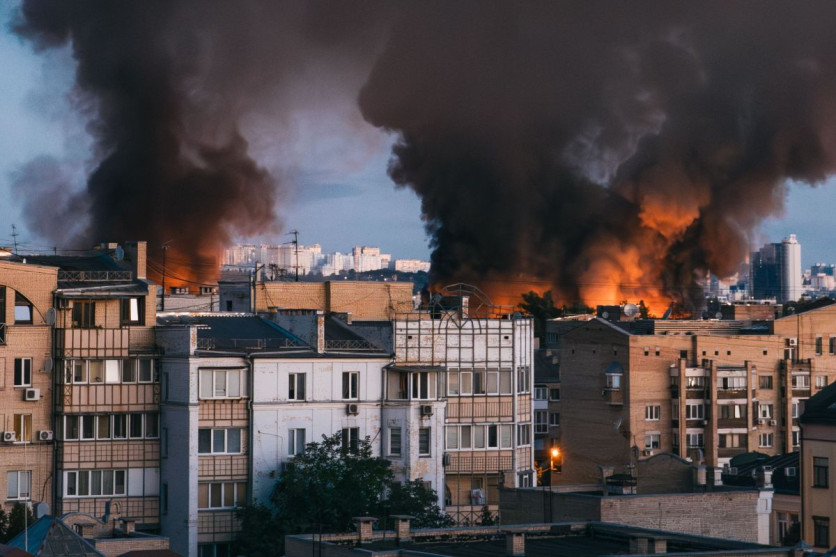
Ukraine's attacks on Russian technology infrastructure have highlighted a vulnerability that could matter far beyond the battlefield: advanced artificial intelligence systems depend on physical facilities that can be damaged, disrupted or forced offline.
Three Yandex data centres were disrupted by drone strikes between 8 and 11 October, according to company statements and Reuters reporting.
The incidents disrupted computing infrastructure used for digital services and AI development, raising questions about how governments should protect the facilities supporting essential technology, particularly when private companies operate infrastructure relied upon by public institutions.
Yandex confirmed that its Sasovo data centre was seriously damaged and shut down following an attack overnight on 7-8 October. The facility, located in Russia's Ryazan region, suffered a fire, and the company said it was assessing the damage before determining whether the equipment could be restored.
Its Kaluga facility was hit the following day, with part of its infrastructure taken out of service. On 11 October, the company reported that its data centre in the Vladimir region had also been shut down after a drone strike. Yandex reported no injuries in the Vladimir incident.
The attacks do not establish that American AI facilities face the same immediate threat. Russia is fighting an active war, and the circumstances differ from those in the United States.
However, the damage illustrates why AI security involves more than protecting software against hackers. Computing systems also rely on electricity, cooling, communications networks and equipment that must remain operational.
For US policymakers, the question is how to maintain essential services if a major computing facility becomes unavailable, whether through physical damage, a power failure or a cyberattack.
Yandex AI Disruption Highlights Data Centre Vulnerabilities
The Sasovo incident was particularly relevant to AI development because the facility housed two of Yandex's three supercomputers used to develop its AI models. The company said it could not yet confirm whether the equipment could be restored.
Reuters reported that the disruption affected online services, while some businesses using Yandex Cloud encountered difficulties accessing their data. In one case, a business reported being unable to access a backup database, but it had not confirmed that any data had been lost.
These effects illustrate the difference between protecting a digital service and ensuring that the infrastructure supporting it remains available. Cybersecurity measures can help prevent unauthorised access, but they cannot by themselves guarantee that servers, power supplies or cooling systems will remain operational after physical damage.
Data centre resilience therefore depends on several layers of protection. Operators can distribute workloads across separate facilities, maintain recoverable copies of data, provide backup power and communications, and establish procedures for restoring services.
However, these measures are effective only if alternative systems have sufficient capacity and can be brought online within the time available.
The location of backup infrastructure also matters. Two facilities may appear separate on a network diagram but still depend on the same electricity supplier, communications route or other essential service. A disruption affecting that shared dependency could undermine both sites.
The United States already has a substantial data centre concentration in northern Virginia. Loudoun County reported approximately 233 data centre buildings covering around 56.5 million square feet as of March 2026, describing the county as having the highest concentration of data centres anywhere in the world.
That concentration makes continuity planning relevant to businesses and public institutions using the region's computing capacity. It does not establish that American facilities are inadequately protected or that an attack comparable to those in Russia is likely.
US AI Security Policy and Critical Infrastructure Preparedness
The US government has outlined measures intended to strengthen the security and reliability of AI used for national security. On 5 June, President Donald Trump signed a memorandum directing the national security enterprise to accelerate AI adoption, use advanced models from multiple vendors and develop high-security computing facilities.
The accompanying White House fact sheet also emphasised secure AI deployment and reducing reliance on a single supplier.
Those measures provide a policy framework for examining infrastructure resilience, although the memorandum should not be taken as evidence that every data centre has specific physical anti-drone protections in place.
The practical question is how its objectives translate into arrangements for keeping essential government functions running during an outage.
A further development came in October, when the White House established the Super Intelligence Force to examine AI risks and opportunities. Reuters reported that Director of National Intelligence Jay Clayton would lead the group, which was expected to produce a report within 120 days.
Its work could provide an opportunity to examine how infrastructure availability fits into national AI security planning, although it has not been established that physical data centre protection is a specific part of its remit.
Counter-drone protection is also subject to specific legal authorities. US law permits designated federal agencies to take certain measures against unmanned aircraft, while qualifying state and local law enforcement agencies have additional powers under statutory conditions and training requirements.
Those provisions do not mean every police department or private data centre operator can independently disable a drone.
For critical computing facilities, preparedness assessments could establish which workloads must continue during an outage, how quickly they need to be restored and whether alternative locations can support them.
Exercises could then test the loss of a site alongside failures involving electricity or communications, rather than assessing each disruption in isolation.
The results would help identify where additional investment, clearer responsibilities or stronger recovery arrangements are justified. Public reporting could outline general readiness without disclosing sensitive technical details, while more detailed assessments could remain restricted to authorised officials.
Ukraine's campaign has provided a real-world example of how physical attacks can disrupt technology infrastructure.
It has not established how a comparable operation would affect the United States, but it has made a practical question harder to ignore: whether essential AI-supported services could continue if the facilities they depend on suddenly became unavailable.
Frequently Asked Questions
- What are the vulnerabilities of AI infrastructure?AI infrastructure is vulnerable to physical damage, disruptions, and cyberattacks, which can affect essential services.
- How can data centers protect against physical attacks?Data centers can distribute workloads, maintain backup systems, and establish recovery procedures to protect against physical attacks.
- What measures has the US government taken to secure AI infrastructure?The US government has outlined measures to strengthen AI security, including accelerating AI adoption, using advanced models, and developing high-security computing facilities.


